Dedicated Servers
PCI DSS Compliant Hosting UK
UK hosting infrastructure that supports PCI DSS compliance for ecommerce and payment processing businesses
UK hosting infrastructure that supports PCI DSS compliance for ecommerce and payment processing businesses
About This Feature
PCI DSS Compliant Hosting UK from Glitch Servers provides infrastructure suited to cardholder data environments - the network and server infrastructure where payment card data is stored, processed, or transmitted. PCI DSS (Payment Card Industry Data Security Standard) requires organisations that handle card payments to maintain a secure infrastructure environment, and the hosting infrastructure is a documented component of any PCI DSS assessment. UK data residency ensures cardholder data stays within UK jurisdiction with documented security controls. Dedicated server options provide hardware isolation for cardholder data environments that require single-tenant infrastructure under PCI DSS Requirement 1. Network-level DDoS protection, firewall management, access logging, and encrypted data transmission support multiple PCI DSS technical requirements. Private VLAN capability enables network segmentation between cardholder data environment and other systems, reducing PCI DSS scope. Our team can provide network architecture documentation, security control evidence, and signed data processing agreements to support your Qualified Security Assessor (QSA) assessment. Note: PCI DSS compliance is a business process responsibility - we provide infrastructure and documentation support, not a PCI-certified managed service.
Key Benefits
Every plan includes these capabilities as standard - no tier-gating, no hidden extras.
Dedicated single-tenant hardware for cardholder data environments - meets PCI DSS Requirement 1 isolation needs
Private VLAN network segmentation isolates cardholder data environment from other systems
DDoS protection, access logging, and encrypted transit support PCI DSS technical security requirements
QSA documentation package: network architecture, security control evidence, signed DPA
Technical Specifications
Real specs on real hardware - not marketing numbers.
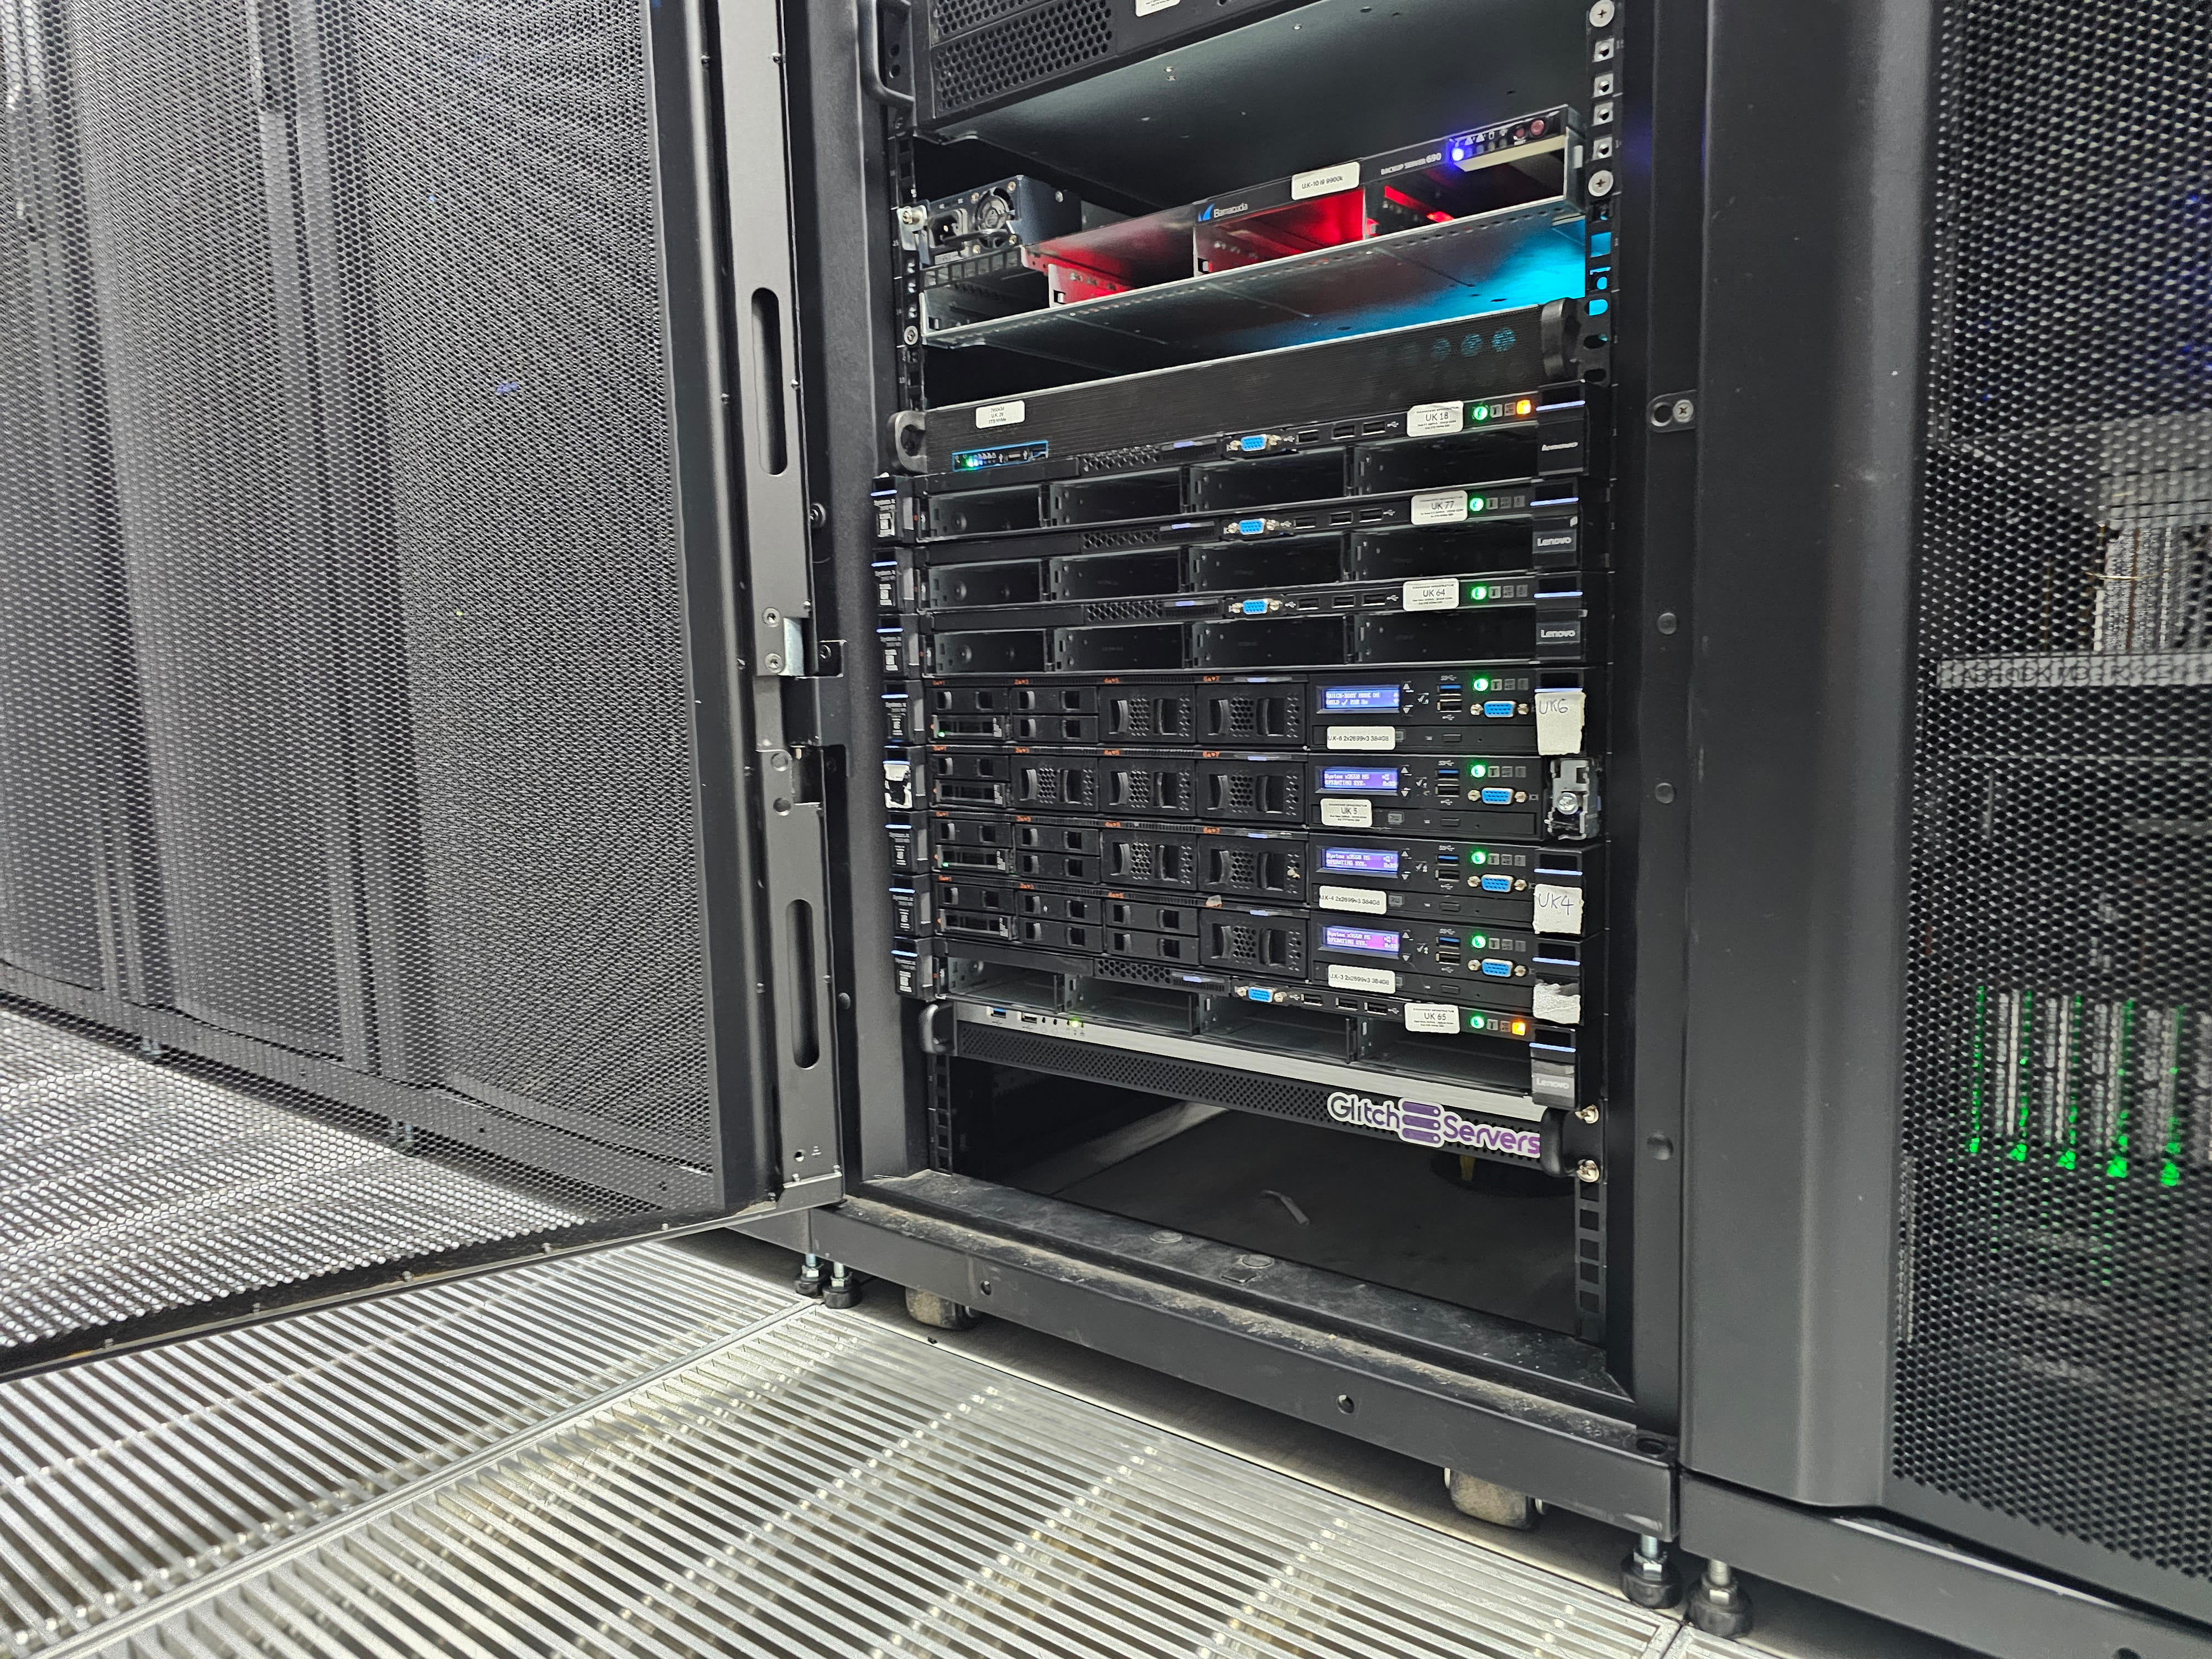
Dedicated servers - single-tenant hardware for PCI DSS cardholder data environment isolation
Private VLAN - network segmentation between CDE and non-CDE systems
UK data residency - cardholder data does not leave UK jurisdiction
Use Cases
This feature is particularly well suited to these workloads and teams.
Online retailers accepting card payments who need to document their infrastructure environment for PCI DSS compliance - dedicated hosting provides the hardware isolation and network segmentation that QSA assessors look for.
Payment technology businesses and fintech companies processing card transactions - UK-hosted dedicated infrastructure with documented security controls provides the evidence base for PCI DSS reporting obligations.
Hotels, restaurants, and retail chains managing card payment data - UK colocation or dedicated hosting provides the documented UK data residency and security controls that their PCI DSS programmes require.
FAQ
Discuss PCI DSS hosting requirements with our team
Dedicated hardware. Network segmentation. UK data residency. QSA documentation.
View Plans →