Cloud VPS
GDPR Compliant Web Hosting UK
All data stored in the UK - UK GDPR compliant infrastructure with documented security controls
All data stored in the UK - UK GDPR compliant infrastructure with documented security controls
About This Feature
GDPR Compliant Web Hosting UK from Glitch Servers provides infrastructure where all data is stored and processed within the United Kingdom, satisfying the UK GDPR requirement that personal data is not transferred outside the UK without adequate safeguards. Following Brexit and the UK's departure from the EU GDPR framework, UK organisations must comply with the UK GDPR - administered by the Information Commissioner's Office - which mirrors EU GDPR requirements while applying to UK-based data controllers and processors. Hosting personal data on UK infrastructure eliminates the need to rely on adequacy decisions or standard contractual clauses for the hosting relationship itself. AS212868 routing through LINX and LONAP keeps UK traffic on domestic network paths without transiting Continental European infrastructure. Documented security controls including network-level DDoS protection, Imunify360 malware scanning for web hosting environments, access logging, and encrypted data transmission support Article 32 technical security measure requirements. We are registered with the ICO as a data processor. Data processing agreements are available for business customers who need to document their processor relationships under UK GDPR Article 28.
Key Benefits
Every plan includes these capabilities as standard - no tier-gating, no hidden extras.
All data stored and processed in the UK - no international transfers in the hosting relationship
ICO-registered data processor - Article 28 data processing agreements available for business customers
Documented security controls: DDoS protection, malware scanning, access logging, encrypted transit
UK-native routing through AS212868 - UK traffic stays on UK network paths via LINX and LONAP
Technical Specifications
Real specs on real hardware - not marketing numbers.
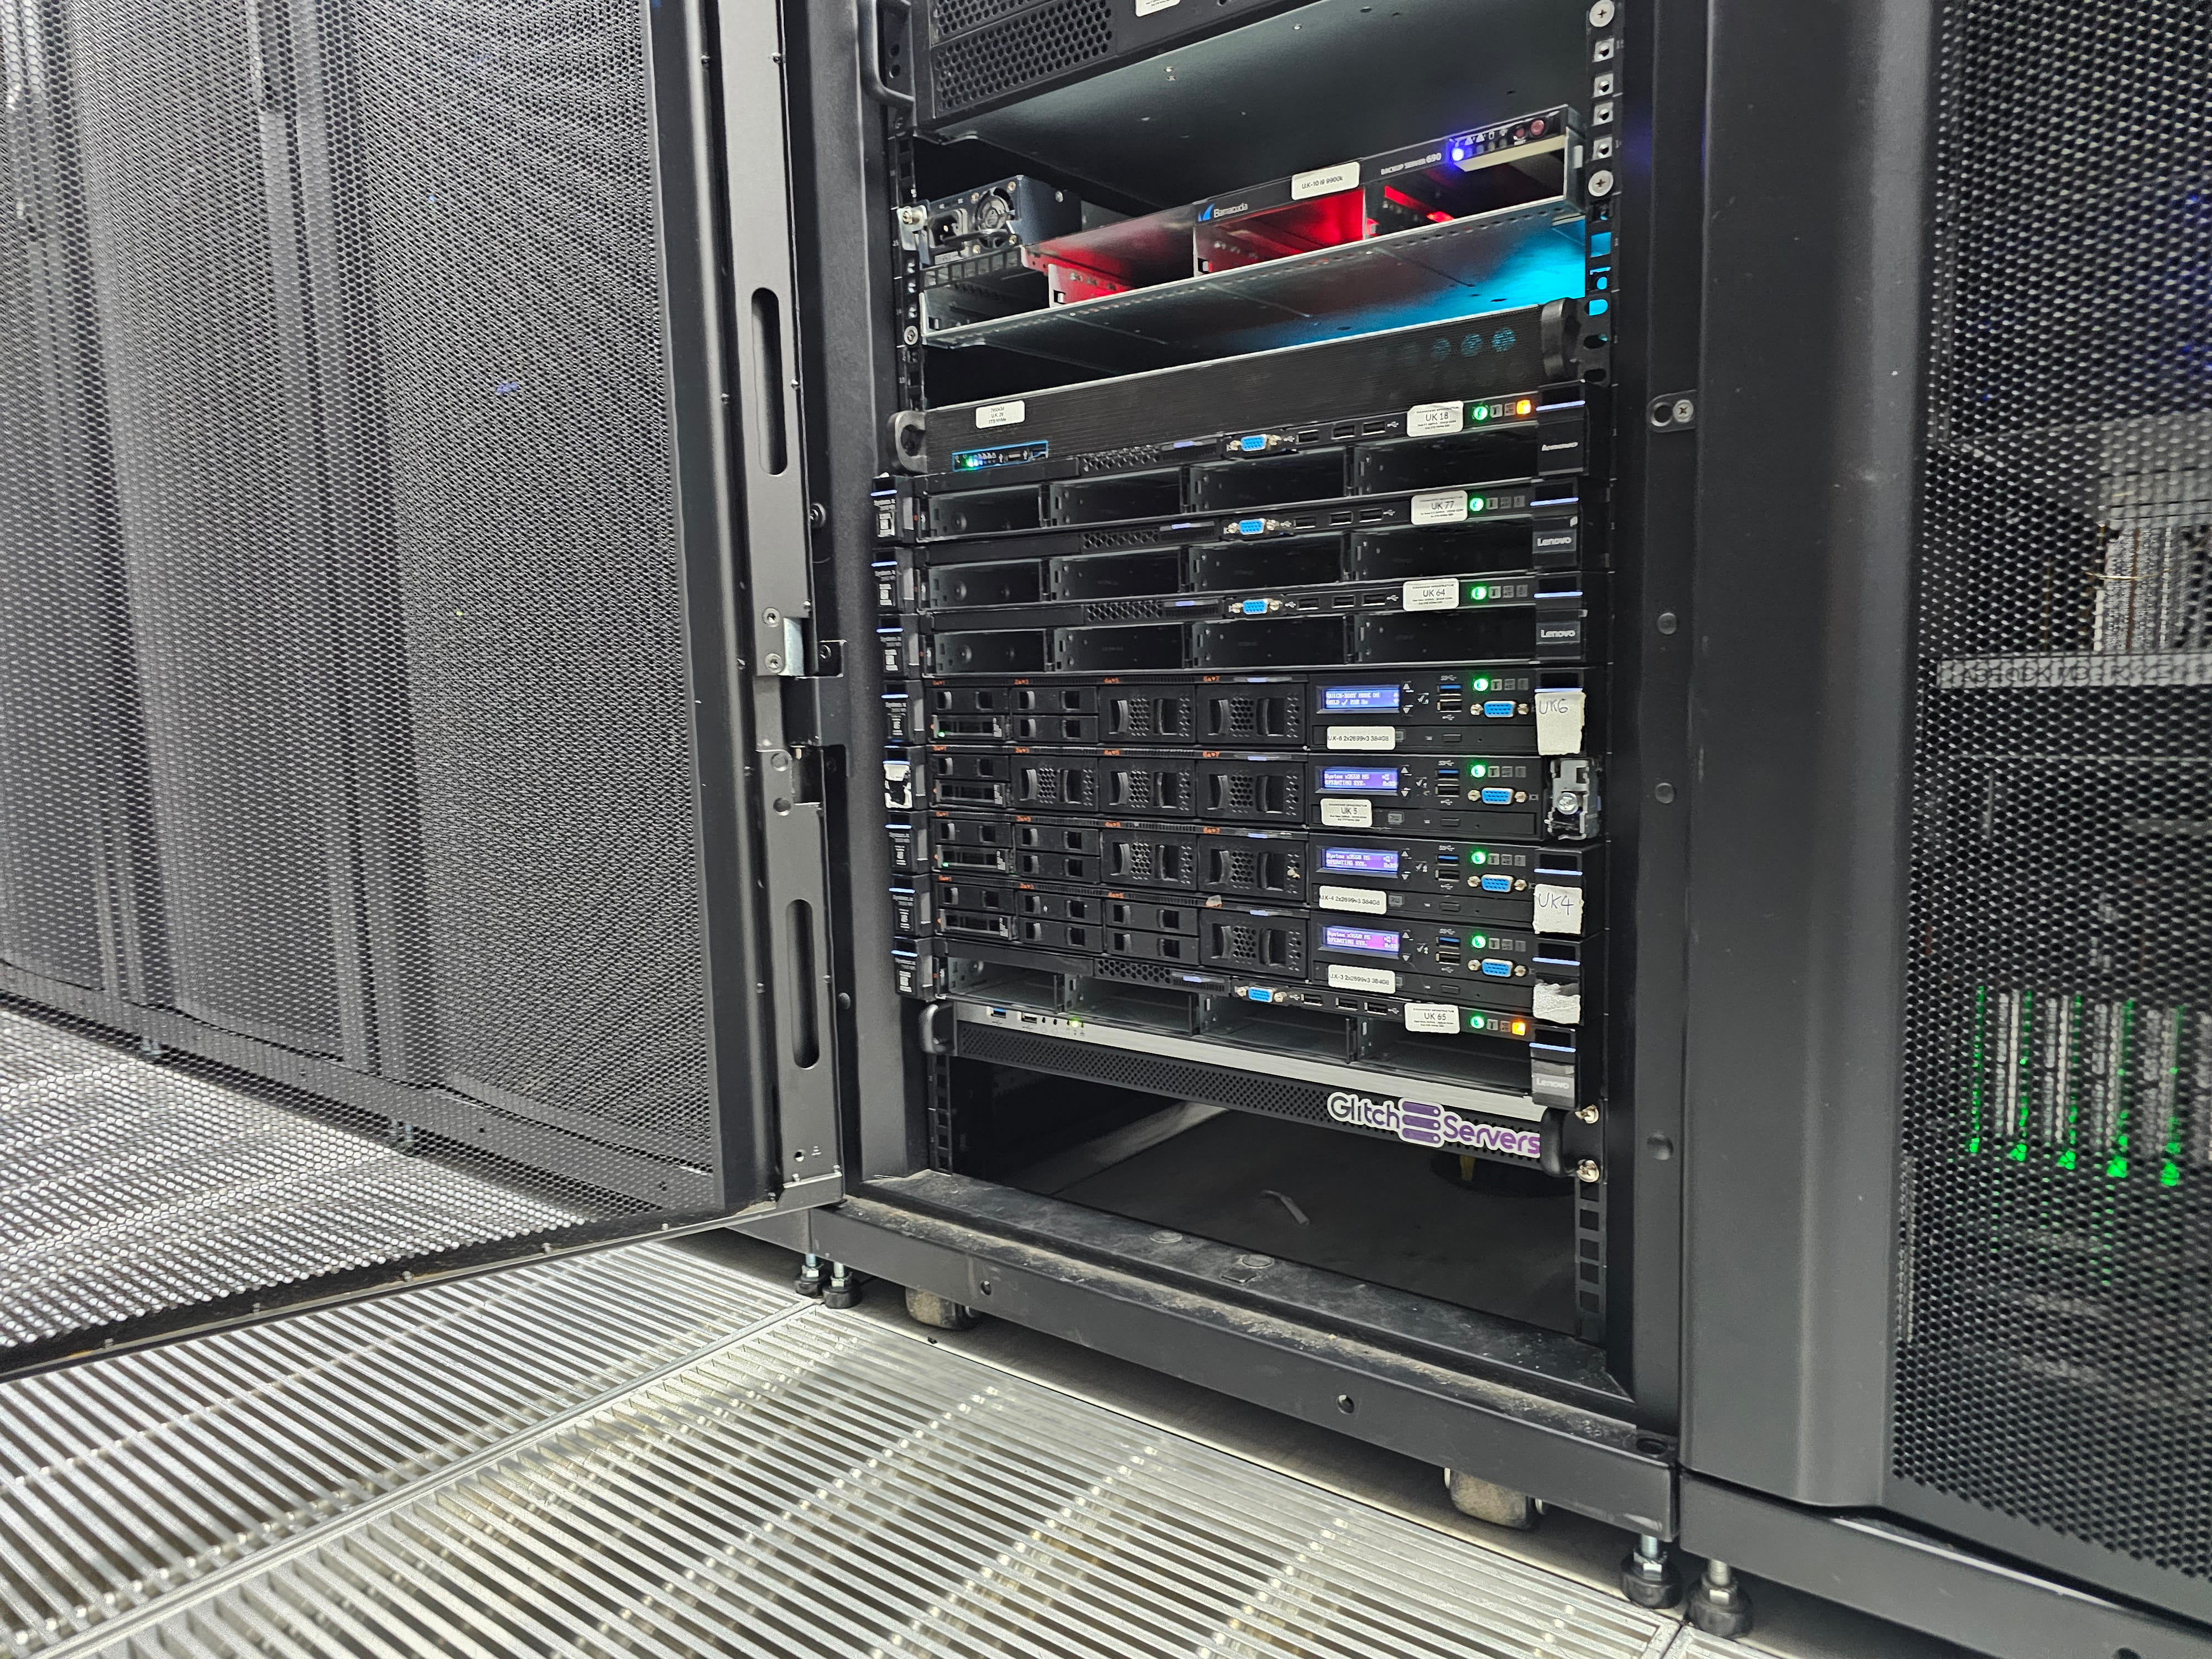
UK data residency - satisfies UK GDPR Article 44 on international data transfers
ICO registered processor - Article 28 DPA documentation available
Encrypted transit, access logging, DDoS protection - Article 32 technical measures
Use Cases
This feature is particularly well suited to these workloads and teams.
Hosting on UK servers keeps processing inside the UK GDPR regime - no international-transfer assessments, standard contractual clauses, or adequacy questions to document.
If your privacy policy promises data stays in the UK, your infrastructure has to match it. UK-owned servers in a UK data centre make that promise true by default.
Processor questions - where is data stored, who can access it, how are breaches notified - get straightforward answers backed by UK data residency and documented security controls.
FAQ
Get UK GDPR compliant hosting from £4.99/mo
UK data residency. ICO registered. DPA available. Documented security controls.
View Plans →