Manual mitigation requires engineering intervention at exactly the worst possible time - during an active attack

DDoS Protected Hosting UK

Always-on 1Tbps DDoS scrubbing across all UK hosting plans - game servers, VPS, and dedicated all protected

DDoS attack traffic scrubbing diagram showing clean traffic passing through

The Problem

Common Challenges for Manual mitigation requires engineering intervention at exactly the worst possible time - during an active attack

These are the issues that consistently come up when Manual mitigation requires engineering intervention at exactly the worst possible time - during an active attack try to scale on the wrong infrastructure.

Challenge 1

DDoS attacks are a commodity threat - botnet-as-a-service lets anyone launch multi-gigabit floods for pocket money

Challenge 2

Many hosts charge DDoS protection as a paid add-on, leaving customers unprotected on standard plans

Challenge 3

DDoS attacks take websites and game servers offline for hours - every minute offline costs revenue and reputation

How We Help

How Glitch Servers Solves This

DDoS Protected Hosting UK from Glitch Servers provides always-on volumetric DDoS mitigation at the network edge - backed by AMD Ryzen hardware, NVMe Gen4 storage, and UK-native routing through AS212868. DDoS attacks have become a commodity threat - botnet-as-a-service platforms let anyone launch multi-gigabit floods against any IP address for a few pounds. Game servers, community platforms, e-commerce sites, and even small business websites are targeted routinely. Our scrubbing infrastructure handles all of it automatically: volumetric floods up to 1Tbps are detected within seconds and filtered upstream of your server, with no action required on your part. Legitimate traffic continues to your server uninterrupted. DDoS protection is not an add-on at Glitch Servers - it is a standard feature of every hosting product we offer.

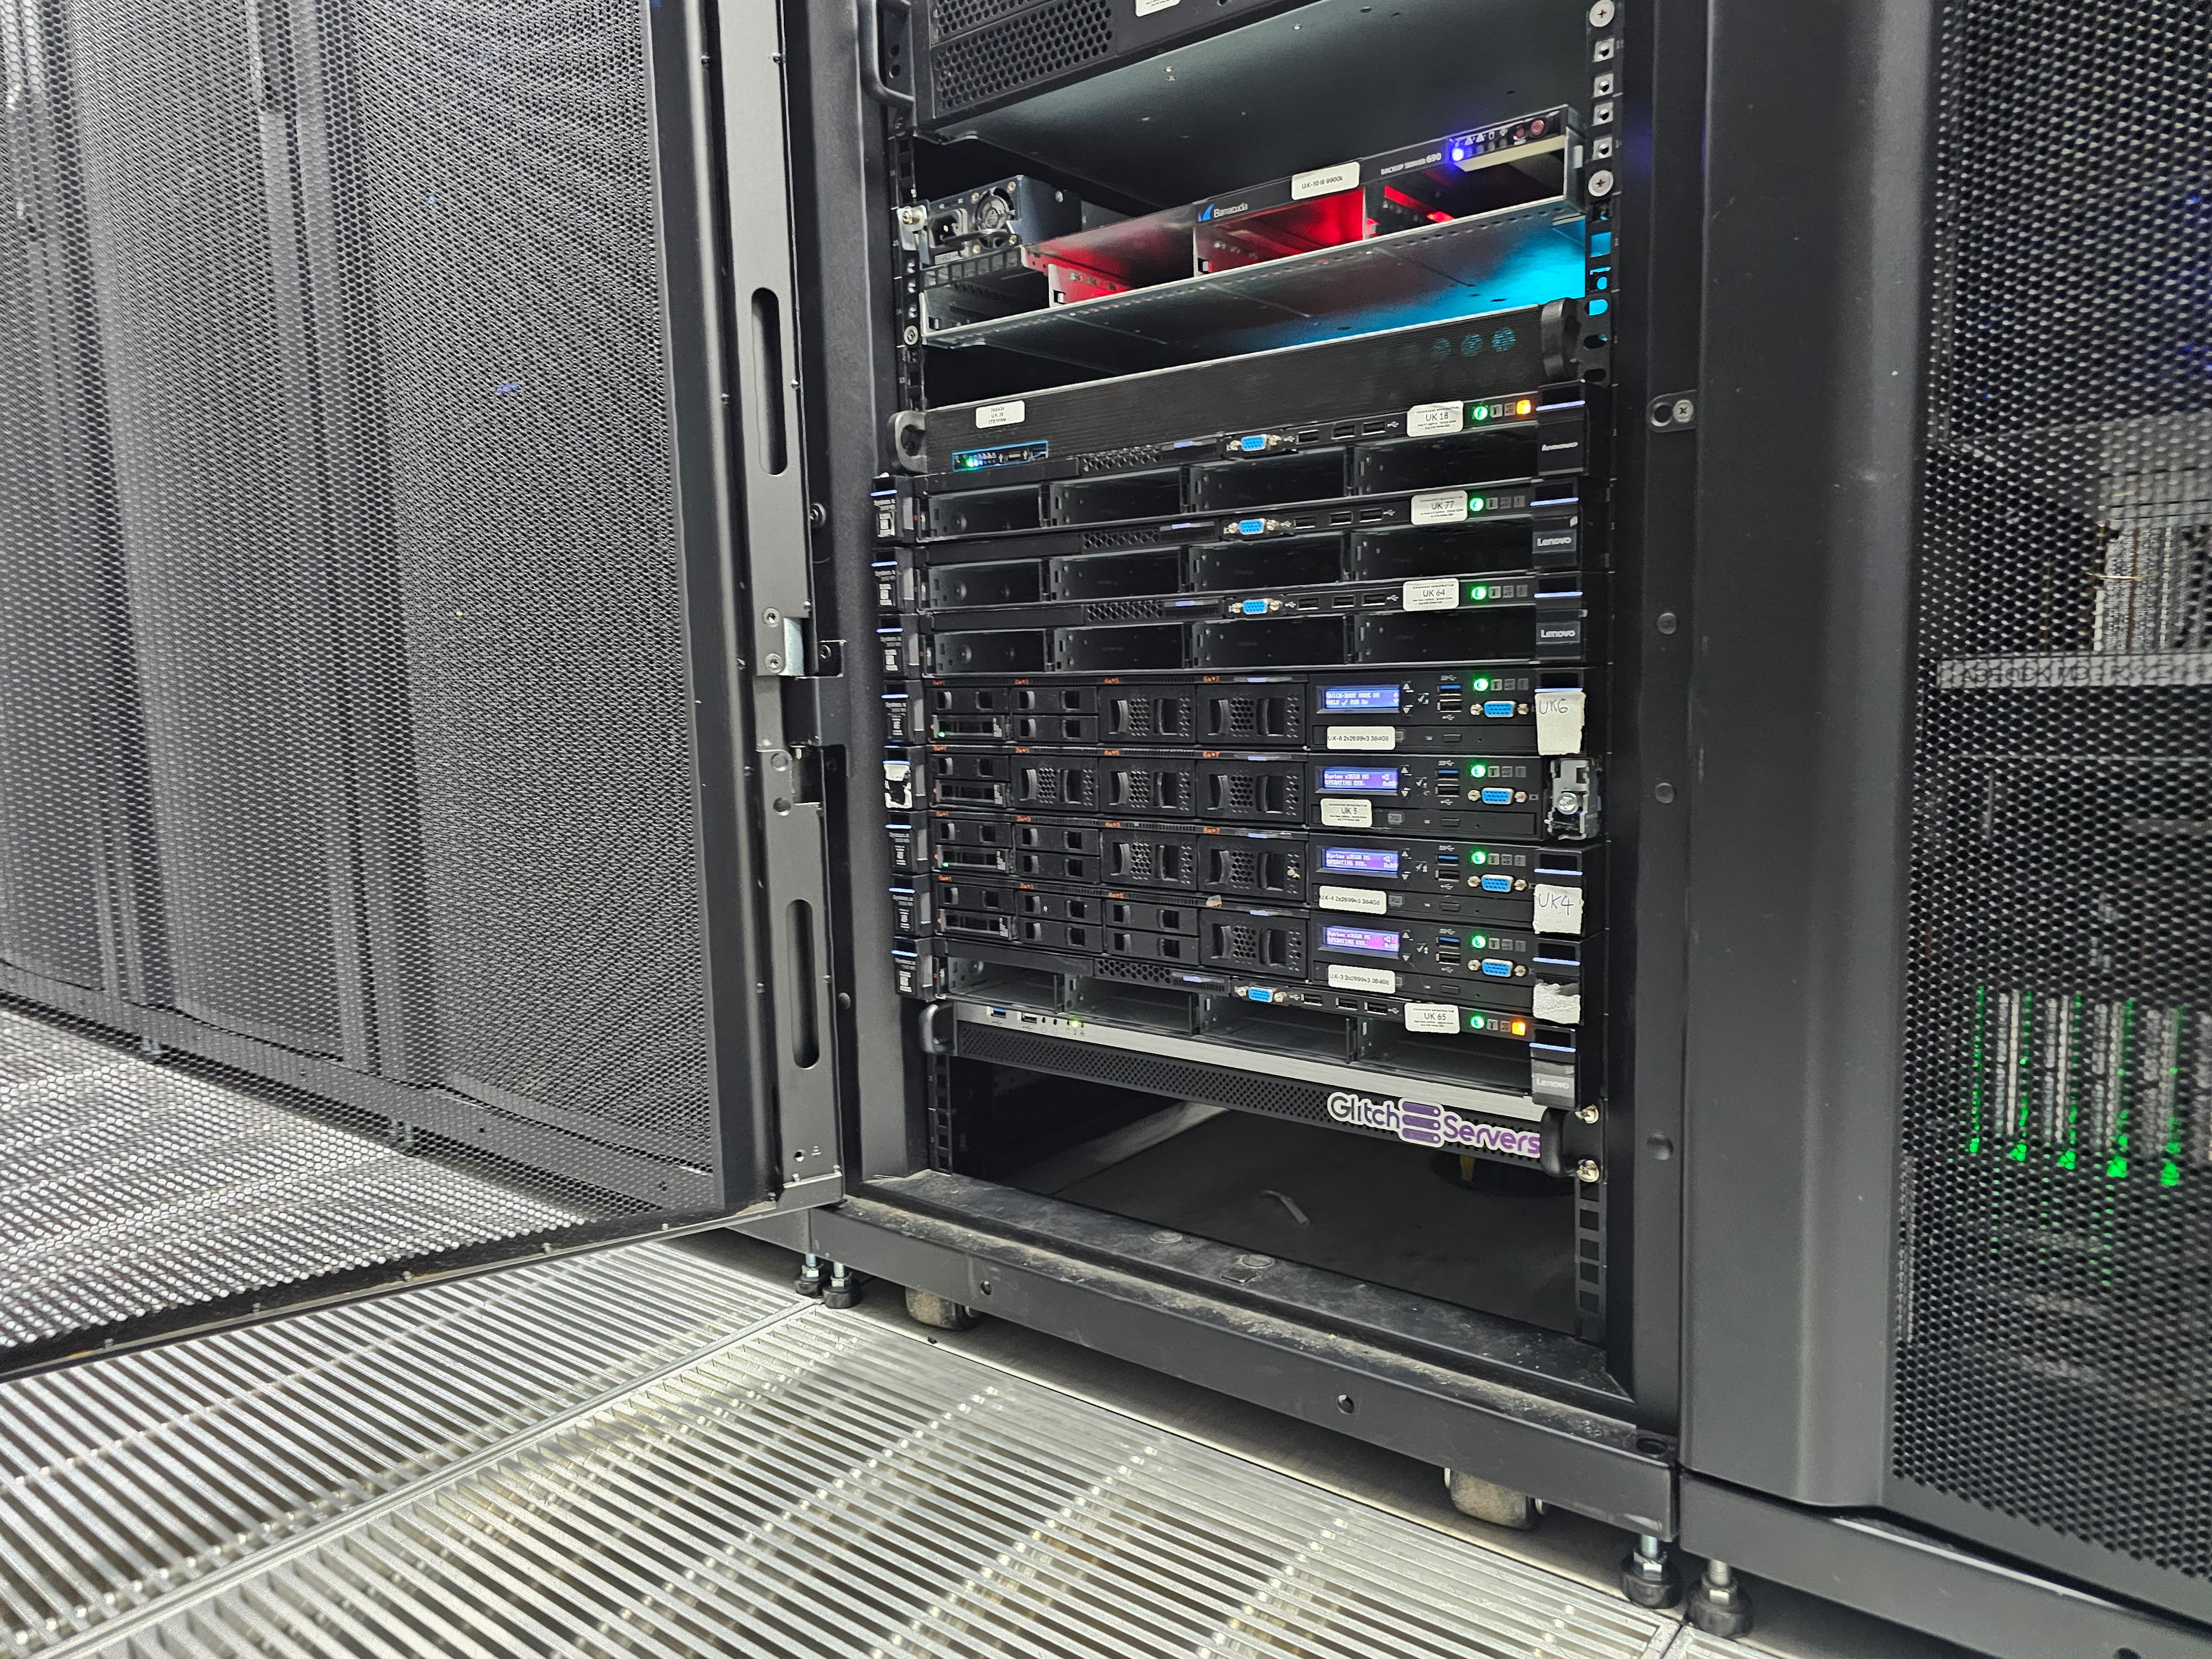
DDoS mitigation at Glitch Servers operates through Corero Smartwall - an inline hardware scrubbing solution that processes traffic at line rate before it reaches the protected server. Unlike cloud-based scrubbing centres that redirect traffic via DNS or BGP, inline mitigation requires zero manual intervention and zero failover delay: protection is always active from the moment traffic enters the network.

AS212868 maintains connectivity to LINX and LONAP with Tier-1 transit through NTT and GTT. The 100G DWDM backbone provides sufficient headroom to absorb large volumetric attacks - typically hundreds of Gbps - without saturating uplinks to the rest of the facility. Attack traffic is dropped at the edge; clean traffic continues to the server without disruption.

All Glitch hosting plans include DDoS protection at no additional charge. Full details on attack mitigation thresholds and protection specifications are on the DDoS protection page.

External resources: LINX (London Internet Exchange) and RIPE NCC (European IP registry).


Many hosts charge extra for DDoS protection or offer inadequate network-level mitigation that doesn't stop sustained attacks
What You Get

Built for Manual mitigation requires engineering intervention at exactly the worst possible time - during an active attack

The features that matter most for your workload, included as standard.

⚡

Automatic detection and response within 5–10 seconds of attack onset without any manual intervention

Always-on 1Tbps DDoS scrubbing upstream of all hosting nodes - attacks filtered before they reach your server

🛡

DDoS protection with no extra cost - included in every plan price, not a paid add-on

Multi-vector mitigation covers UDP floods, SYN floods, TCP state exhaustion, and HTTP application-layer attacks

🔧

Always-On Protection

Automatic detection within 5–10 seconds of attack onset - no manual intervention, no tickets during an attack

💰

1Tbps Capacity

Zero configuration required - DDoS protection activates automatically and requires no changes to your application or DNS

Trust Signals

Infrastructure You Can Rely On

99.9%
Uptime SLA
100G
Backbone Capacity
AS212868
Own Network ASN
24/7
UK-Based Support
DDoS protection monitoring dashboard with attack visualisation

FAQ

Frequently Asked Questions

Our scrubbing infrastructure sits upstream of all hosting nodes. In normal conditions it inspects traffic at line rate without adding latency. When an attack pattern is detected, malicious traffic is dropped at the scrubbing layer before it reaches your server.
In normal operation, latency through our scrubbing layer is negligible - typically under 0.5ms additional overhead. During an active attack, slight latency variation is possible as traffic is inspected more deeply, but legitimate sessions remain active.
Our scrubbing handles volumetric attacks (UDP floods, SYN floods, ICMP floods), protocol attacks (fragmentation attacks, TCP state exhaustion), and common application-layer attacks (HTTP floods). Multi-vector attacks are also handled by our adaptive filtering.

Get DDoS-protected hosting from £4.99/mo

1Tbps scrubbing included on all plans. No setup. No extra fees.

View Plans →